Vulnerability Management for Embedded Devices
Embedded products ship with firmware, third-party components, open-source packages, and supplier code that stays in the field for years. Standard IT scans can’t show which CVEs are reachable or exploitable in a firmware image. ONEKEY’s firmware-first vulnerability management cuts through CVE noise and keeps exposure and compliance under control.
Industry Leaders Rely on ONEKEY


Why Embedded Device Teams Struggle with Vulnerability Management
Traditional scanners target servers and cloud workloads. Embedded products ship as firmware with supplier code. A vulnerability management tool for embedded devices analyzes what’s actually inside.
No Visibility into Third-Party Firmware Components
Your product likely includes code from internal teams, suppliers, chipset vendors, and open-source projects, often as binaries with no source or dependency records. This hides component ownership, slows releases, weakens supplier assurance, and complicates audits.
CVE Overload Without Firmware Context
CVE feeds keep growing, but not every CVE affects your firmware. Generic matching creates noise and delays real fixes. Your team needs to reduce false positives, prioritize by real product impact, and highlight exploitable vulnerabilities. The result is a smaller, clearer list of risks your engineers can act on.
Compliance Deadlines Require Documented Proof – CRA, IEC 62443 & NIS-2
Product cybersecurity regulations, including CRA, IEC 62443, and NIS-2, expect documented proof. You must track, assess, prioritize, and handle vulnerabilities. Your compliance team needs records of SBOMs, vulnerability status, remediation plans, and release history. Manual spreadsheets can’t keep pace.
Powerful Capabilities for Real Firmware Risk Detection
CVE Prioritization Based on Your Actual Firmware
A component-level CVE match does not always mean a vulnerability affects the product. ONEKEY evaluates firmware evidence to find relevant vulnerabilities. It filters findings that seem not affected. Teams focus remediation and compliance on real product risk.

Post-Deployment Firmware Monitoring with the Digital Cyber Twin
Risk keeps changing after a product ships, as new CVEs appear and firmware versions vary across markets. ONEKEY’s Digital Cyber Twin gives you a living security view of every version, so you can compare releases and spot affected products.

Automated SBOM Generation from the Binary
ONEKEY identifies software components in firmware and builds or enriches an SBOM. Compliance teams get a stronger basis to understand third-party software and track it across versions. The inventory also supports vulnerability and regulatory workflows.

How ONEKEY Solves Vulnerability Management for Embedded Devices
ONEKEY moves your team from generic CVE lists to firmware-specific risk insight. It analyzes embedded firmware, generates SBOMs, verifies vulnerabilities, and monitors products after release. This turns product security into a repeatable workflow built on real firmware evidence.

Binary-Level Firmware Analysis – No Build System, No Source Code Required
ONEKEY analyzes firmware at binary level, so your team never needs source code or a build system. This is essential for closed supplier firmware or undocumented legacy software. Analysis uncovers hidden packages, outdated libraries, configuration weaknesses, and hard-coded risks, giving your team a direct view that speeds up triage.

Automated SBOM Generation Directly from the Binary
ONEKEY generates SBOM data directly from firmware binaries, identifying packages, versions, and dependencies even when supplier data is incomplete. This gives your team a reliable foundation for release reviews, customer requests, and regulatory documentation. SBOM Audit links that visibility with proof, so your SBOM drives decisions.

CVE Prioritization Based on Your Actual Firmware – Not Generic Component Lists
ONEKEY checks whether each detected vulnerability actually matters in your firmware, filtering out findings that are irrelevant, mitigated, or not exploitable. This cuts more than 60% of false positives and saves engineering time. Each result explains why a CVE matters and what to do next, so PSIRT managers can focus on real risk.
How ONEKEY Cuts CVE Noise for Embedded Devices
Generic scanners match CVEs against component names and leave your team to sort out what is actually exploitable in the firmware. For embedded devices with supplier code, long lifecycles, and dozens of versions in the field, that manual triage never ends. ONEKEY automates the workflow through binary-level analysis of the firmware image itself. You get a repeatable path from upload to prioritized, documented remediation.
The process starts by uploading the firmware image into the platform. You do not need source code, a build system, or supplier documentation, which is essential for closed third-party firmware and undocumented legacy software. Each product version can be analyzed as it ships, not as it was declared. This gives your team a direct view of the software that actually runs on the device.
ONEKEY analyzes the compiled firmware to identify packages, versions, and dependencies and builds an SBOM for the release. Known CVEs are matched against those components, and zero-day patterns, configuration weaknesses, and hard-coded risks are detected alongside them. Hidden and inherited components surface even when supplier data is incomplete. Your team starts from a complete picture instead of a partial inventory.
ONEKEY checks whether each detected CVE actually matters in your firmware and filters out findings that are irrelevant, mitigated, or not exploitable. This removes more than 60% of false positives before anyone looks at the list. Remaining findings are prioritized by real product impact, and each result explains why it matters and what to do next. Engineering and PSIRT teams spend their time on fixes rather than triage.
Confirmed findings move into remediation with clear ownership and status across products and versions. Evidence for CRA, IEC 62443, and NIS-2 is generated from the same data, so compliance documentation does not become a separate project. After release, ONEKEY's Digital Cyber Twin monitors every firmware version for new CVEs and component changes. Your team stays in control across long product lifecycles.
FACTS & Figures
FACTS & Figures
90% Less Vulnerability Effort
Reduce manual triage work and help your security team prioritise real firmware threats faster
ROI in Under 3 Months
Lower triage time and cost while keeping existing product workflows moving
Save 3+ Years of Analyst Time
Eliminate irrelevant CVEs and reduce manual review effort when scanning 50 firmware images annually
Start Detecting Embedded Vulnerabilities in Minutes
Upload firmware, inspect components, and review findings without rebuilding the product. Move from CVE noise to focused remediation, faster.

Why Customers Trust Us

“ONEKEY helps us to uncover critical vulnerabilities in embedded devices in a fully automated way. This allows us to target manual testing efforts more efficiently on business logic issues.“

“We use ONEKEY to check every piece of software for potential risks before it even reaches release candidate status, at which point any issues are immediately analyzed and fixed. This allows us to effectively secure new features and interfaces.”

“We provide best-in-class services to our IoT customers, helping them ensure security throughout their entire product lifecycle. So naturally we want to deliver continuous firmware monitoring and vulnerability assessments using the best tools and solutions in the business. ONEKEY's automated firmware analyses help us to deliver our services efficiently and with unparalleled quality.“

“ONEKEY’s automated binary software analysis simplifies product security at Snap One by reducing manual efforts while increasing transparency and confidence. We enjoyed a smooth onboarding experience and highly recommend the excellent support from a team of experts.”


“ONEKEY’s capabilities and security expertise made it a truly eye-opening experience to work with them.”

Embedded Device Security Features Built Around Your Workflow
ONEKEY supports your full product security workflow, not one isolated scan. It connects engineering, PSIRT, and compliance teams around the same firmware evidence, so security fits the way your team already works.

Focus on Vulnerabilities That Actually Matter
ONEKEY connects CVEs, SBOMs, exploitability, and real firmware impact in one place. Your team spots real firmware threats, cuts false positives, and prioritizes what truly matters across every product and version.
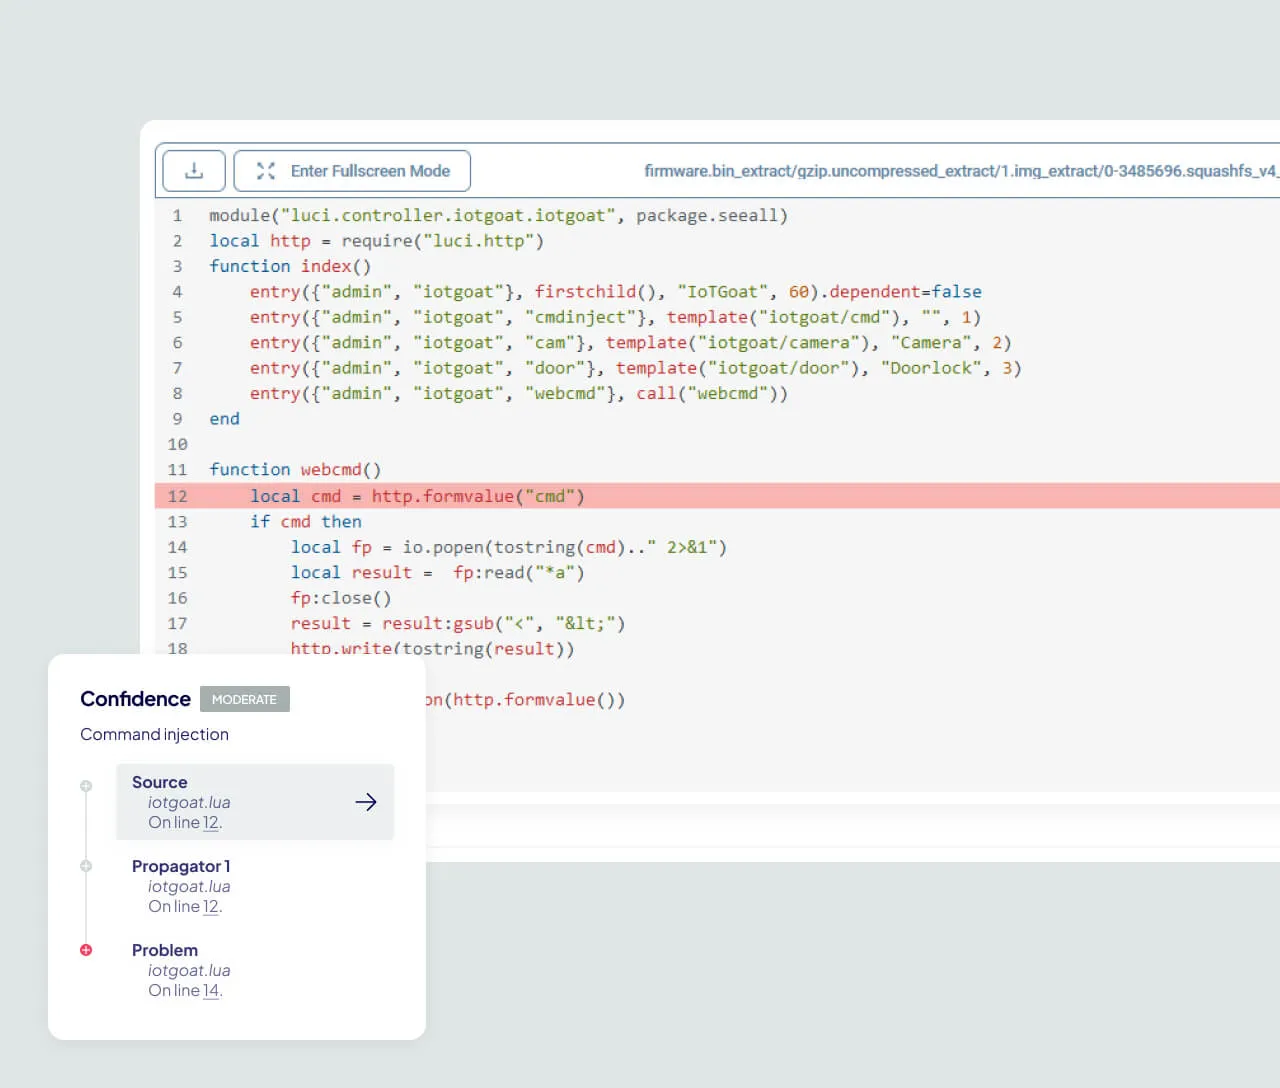
Respond Fast to Critical Threats
Zero-day response needs both speed and context. ONEKEY helps you quickly assess whether a newly disclosed issue affects your firmware and where to act, so a public vulnerability doesn’t turn into panic.

Streamline Compliance Management
Compliance gets easier when your evidence is already structured. ONEKEY connects SBOMs, vulnerability findings, remediation status, and lifecycle monitoring to support CRA, IEC 62443, NIS-2, and other product cybersecurity requirements.
FAQs
Get detailed answers to the most common questions on safeguarding your connected products.

What is vulnerability management for embedded devices?
Vulnerability management for embedded devices is the process of finding, assessing, prioritizing, and tracking vulnerabilities inside connected products and firmware. It focuses on the software components that ship within a device and supports monitoring after deployment.
How does ONEKEY analyze firmware without source code?
ONEKEY uses binary-level firmware analysis to inspect firmware images directly. It detects components, versions, vulnerabilities, and security-relevant details without needing source code. This approach is especially useful when supplier records or build systems are not available.
How is embedded device vulnerability management different from traditional IT scanning?
Traditional IT scanning focuses on reachable systems, network services, and patch status. Embedded device vulnerability management focuses on firmware content, binary analysis, SBOMs, and product lifecycle evidence. It requires deeper product context because devices often remain deployed for many years.
Which compliance standards does ONEKEY support for embedded devices?
ONEKEY supports workflows aligned with CRA, IEC 62443, and NIS-2 requirements. It helps teams generate SBOMs, track vulnerabilities, and maintain structured evidence. This makes audits and customer security reviews easier to manage.
What is a Digital Cyber Twin?
A Digital Cyber Twin is a live security model of your product firmware. It tracks components, vulnerabilities, and risk changes over time. This gives your team better visibility after products are released.


