Firmware Compliance Solutions for Connected Products
Your connected products must meet growing cybersecurity requirements across markets, industries, and product lines. ONEKEY replaces manual checklists with automated evidence, continuous monitoring, and clearer control, helping you prove firmware security compliance across CRA, IEC 62443, RED, and NIS2.
Industry Leaders Rely on ONEKEY


Why Firmware Compliance Trips Up Manufacturers
Firmware compliance is not the same as IT compliance. Your team must prove what is inside each product, how risks are handled, and whether every firmware version meets the right standards. That requires product-level evidence, not only policies, checklists, or enterprise controls that never inspect the firmware.
GRC and IT Tools Don’t See Your Firmware
GRC and IT tools help manage policies, controls, and enterprise risk. They do not usually inspect firmware binaries or prove which components are inside a connected product. Your team may have a policy that says products must meet cybersecurity rules. The harder question is whether each shipped firmware version actually meets them. Firmware security compliance needs evidence from the firmware itself, not claims on paper.
Manual Evidence Doesn’t Scale
Manual evidence collection can work for one product or one audit. It breaks down when you manage many product lines, firmware versions, suppliers, and markets. Spreadsheets, shared folders, and email trails create inconsistent records across SBOMs, vulnerability reports, remediation status, and audit exports. Manual work also makes compliance drift harder to detect.
Fast-Moving Regulation Across Frameworks
Cybersecurity regulation is moving quickly for connected products. CRA, IEC 62443, and ETSI EN 303 645 all increase the need for structured product security evidence, and requirements often overlap. A single product may need proof for vulnerability handling, secure configuration, update processes, and lifecycle monitoring.
Firmware Intelligence Behind Every Compliance Move
ONEKEY builds compliance into the full product lifecycle. It supports SBOM generation, vulnerability analysis, zero-day detection, compliance mapping, and post-deployment monitoring, all from direct firmware analysis. Product, compliance, engineering, and PSIRT teams work from the same evidence, so every firmware version can be checked and documented without manual overhead.
Analyze Firmware Without Source
ONEKEY analyzes firmware binaries directly. Your team does not need the original source code, build system, or complete supplier documentation to inspect what is inside a product. This matters when supplier firmware arrives as a closed file. Binary-level analysis identifies components, vulnerabilities, license risks, and compliance gaps, showing what was actually shipped and not only what was declared. That makes firmware compliance solutions more reliable for real product environments.
Spot High-Risk Weaknesses Before They Spread
Zero-day detection helps your team identify high-risk weaknesses before they appear in standard CVE workflows. ONEKEY analyzes embedded firmware to surface critical issues that signature-based tools often miss. This gives PSIRT and engineering teams more context when urgent threats appear, so they can prioritize remediation, track affected firmware versions, and document their response.
Audit-Ready in Minutes
Audit preparation drags when evidence is scattered across tools and teams. ONEKEY generates audit-ready compliance bundles with evidence, vulnerability details, SBOMs, and status in one place. Your team can export in PDF, JSON, or CSV and share the right detail with auditors and leadership.
How ONEKEY Automates Firmware Compliance at Scale
ONEKEY automates firmware security compliance across the connected product lifecycle. It analyzes firmware at binary level, maps findings to regulatory requirements, generates evidence, and tracks compliance status over time. This helps your team move from slow, manual audit preparation to scalable workflows that keep every product version aligned with evolving standards.

End-to-End Regulatory Coverage
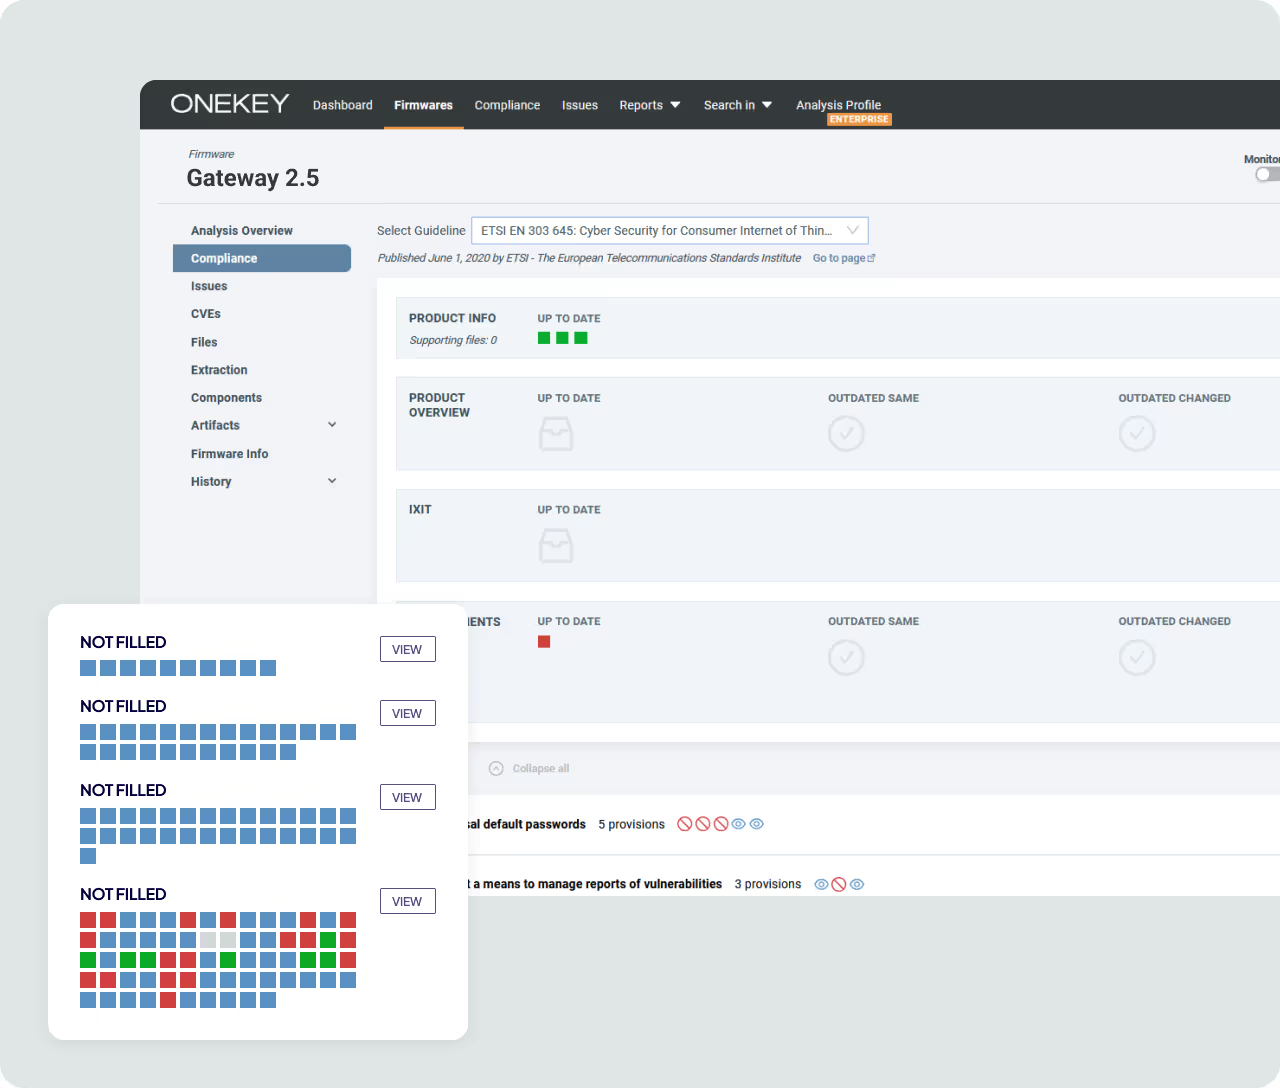
ONEKEY’s compliance workflows support requirements linked to CRA, IEC 62443, ETSI EN 303 645, RED, NIS2, and UN Regulation R155 in one platform. For each requirement, your team can see what is met, violated, not applicable, or needs manual validation, even as regulations evolve or differ across product lines. You can generate audit-ready compliance bundles in PDF, JSON, or CSV, complete with evidence, vulnerability details, and SBOMs. This drastically cuts manual effort and keeps teams ready for audits, customer requests, and certification at any time.

SBOM Management as Your Compliance Base
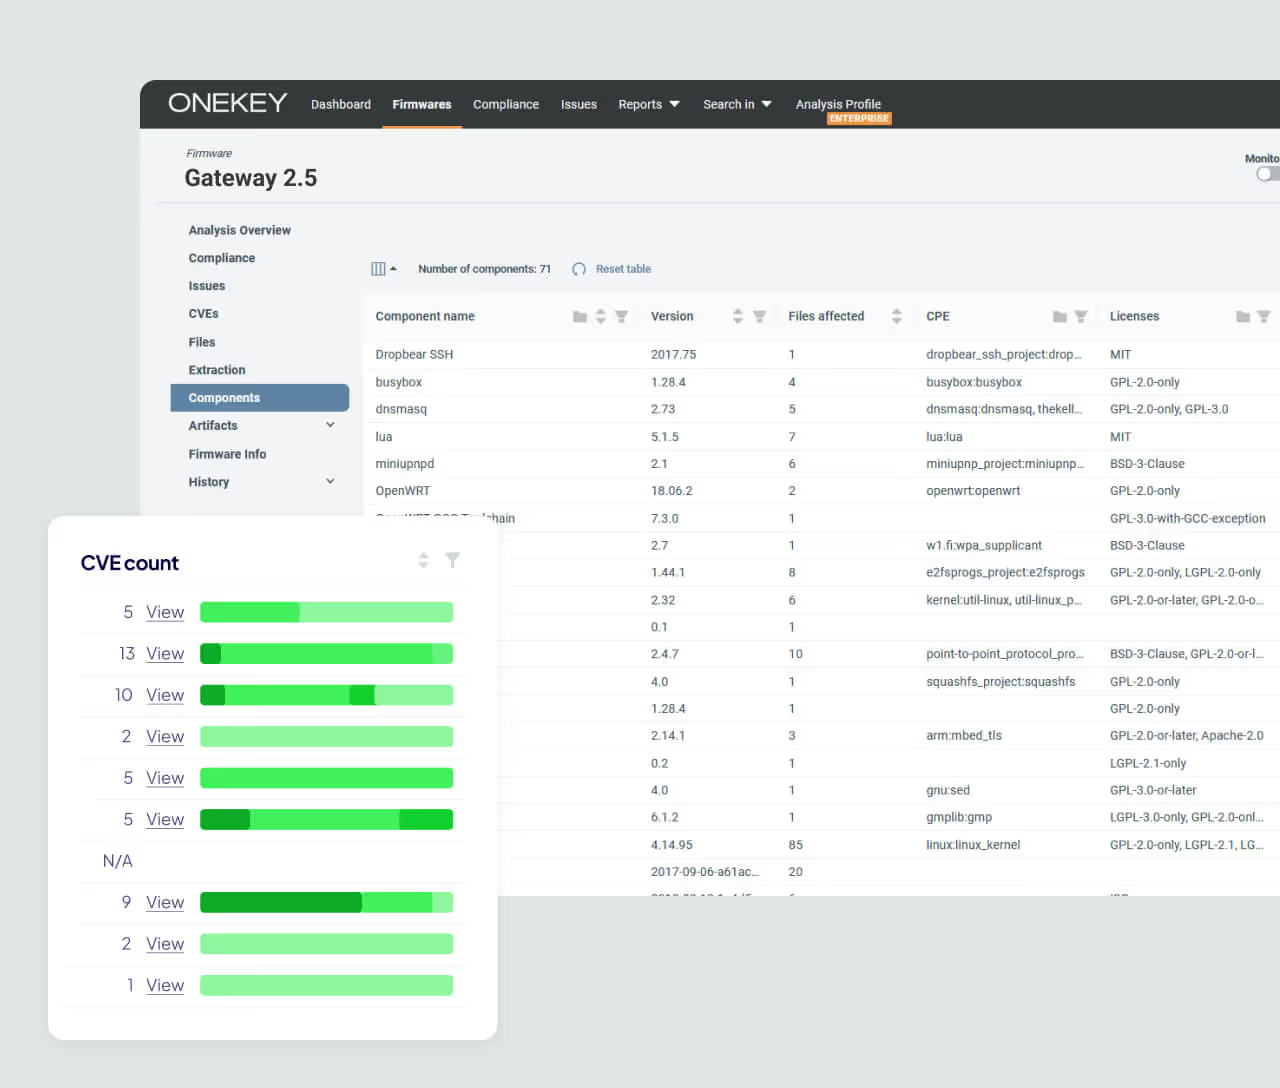
Accurate compliance starts with visibility. ONEKEY generates and normalizes SBOMs directly from binary firmware, even when source code or supplier documentation is incomplete. Every open-source, third-party, and proprietary component is identified and cataloged, then linked to the vulnerabilities and requirements your team must meet. A strong SBOM turns technical data into evidence.

Stay Compliant Over Time
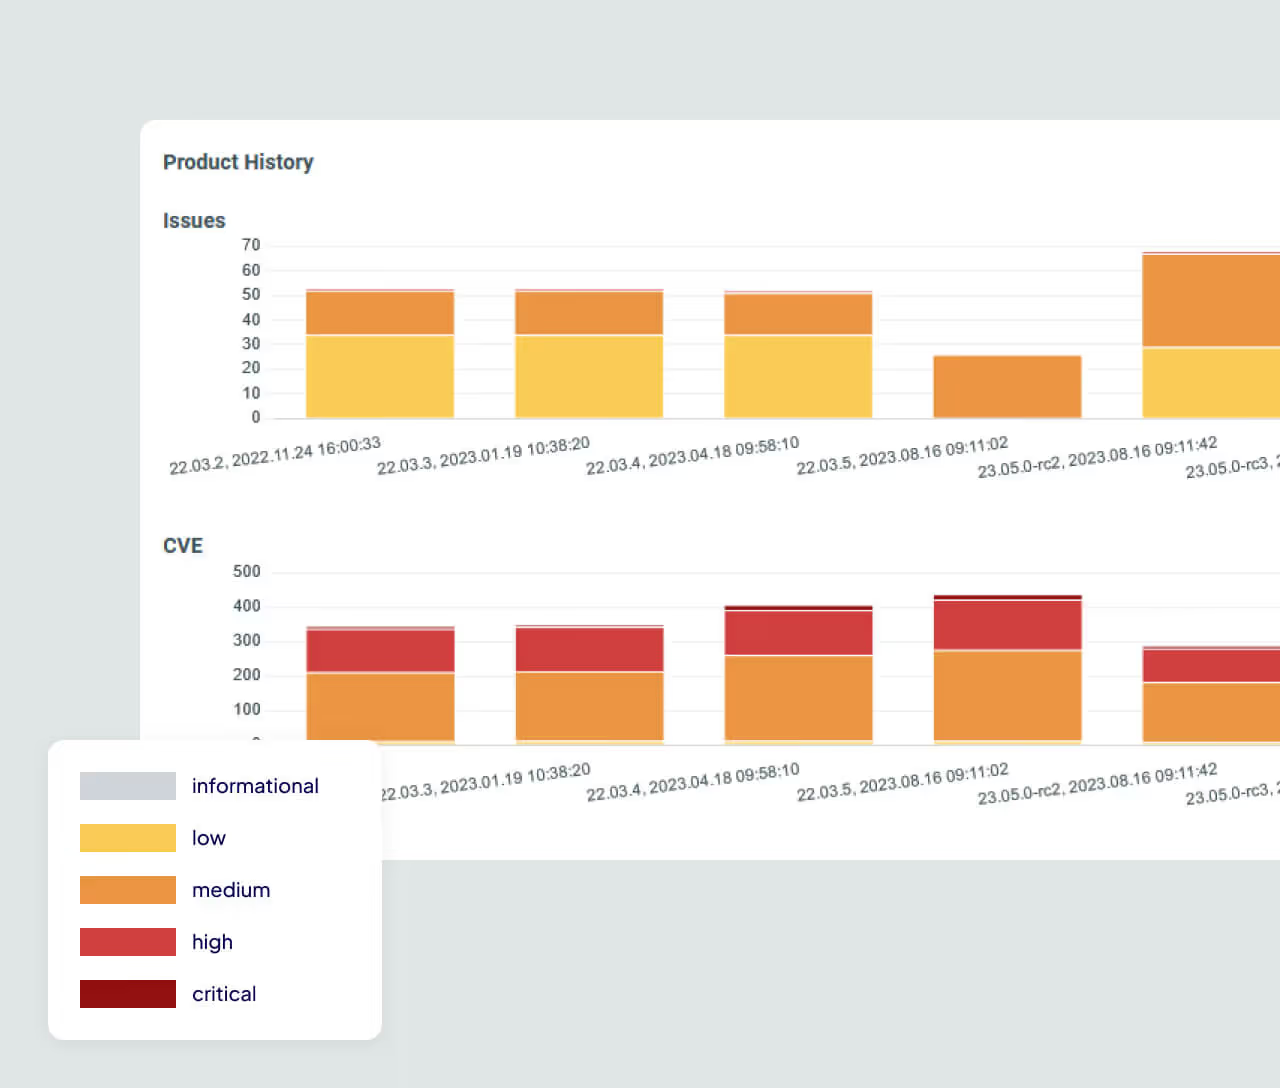
Compliance should not stop at release. Firmware changes, new CVEs appear, supplier components age, and regulations evolve. ONEKEY’s Digital Cyber Twin monitors compliance status across product versions so gaps do not stay hidden, even for long-lived connected products.
How ONEKEY Turns Firmware Into Compliance Evidence
Compliance teams often work from policies, checklists, and supplier declarations that say little about the firmware actually shipped. Mapping that evidence to CRA, IEC 62443, or RED by hand is slow and breaks down across product lines and releases. ONEKEY automates the process through binary-level analysis that maps findings directly to regulatory requirements. This gives you a repeatable path from firmware image to audit-ready evidence.
The process starts by uploading the firmware image into the platform. You do not need source code, build systems, or complete supplier documentation to begin. This is especially useful for supplier firmware that arrives as a closed file or for legacy products with limited records. Every compliance check that follows is based on the software actually inside the product.
ONEKEY analyzes the compiled firmware to build a complete SBOM and identify known vulnerabilities, zero-day patterns, and open-source license obligations. Hidden components, outdated packages, and insecure configurations surface even when they were never declared. The result is a product-level evidence base that generic GRC and IT tools cannot provide. Compliance, engineering, and PSIRT teams work from the same findings.
The ONEKEY Compliance Wizard maps analysis results to the requirements of CRA, IEC 62443, ETSI EN 303 645, RED, NIS2, and UN Regulation R155. For each requirement, you see whether it is met, violated, not applicable, or needs manual validation. Overlapping provisions across frameworks are handled in one view instead of separate spreadsheets. Gaps become visible before an auditor or customer asks about them.
Once the mapping is complete, the platform generates an audit-ready compliance bundle with evidence, vulnerability details, SBOMs, and status in PDF, JSON, or CSV. The bundle can be shared with auditors, customers, and leadership as part of certification and review workflows. ONEKEY's Digital Cyber Twin then monitors each firmware version for new CVEs and changes, so compliance status stays current after release. You maintain proof across the full product lifecycle.
FACTS & Figures
FACTS & Figures
80% Less
of Audit Preparation Time
70% Earlier
Compliance Gap Detection
3x More
Compliance Oversight Without Extra Headcount
Achieve Continuous Firmware Compliance
Replace manual spreadsheets and fragmented audits with automated, scalable workflows. ONEKEY builds compliance into the full product lifecycle, from SBOM generation to compliance mapping and monitoring, keeping you aligned with global standards.

Why Customers Trust Us
“ONEKEY’s automated binary software analysis simplifies product security at Snap One by reducing manual efforts while increasing transparency and confidence. We enjoyed a smooth onboarding experience and highly recommend the excellent support from a team of experts.”

“We use ONEKEY to check every piece of software for potential risks before it even reaches release candidate status, at which point any issues are immediately analyzed and fixed. This allows us to effectively secure new features and interfaces.”

“We provide best-in-class services to our IoT customers, helping them ensure security throughout their entire product lifecycle. So naturally we want to deliver continuous firmware monitoring and vulnerability assessments using the best tools and solutions in the business. ONEKEY's automated firmware analyses help us to deliver our services efficiently and with unparalleled quality.“


“ONEKEY’s capabilities and security expertise made it a truly eye-opening experience to work with them.”


“ONEKEY helps us to uncover critical vulnerabilities in embedded devices in a fully automated way. This allows us to target manual testing efforts more efficiently on business logic issues.“

Ship Compliant, Cybersecure Products with Confidence
Compliance evidence is only as strong as the firmware data behind it. ONEKEY connects SBOMs, vulnerability intelligence, and license data in one platform, so every compliance claim can be traced back to the product. That keeps audits, customer reviews, and certifications on schedule.
SBOM Management
ONEKEY generates, imports, and normalizes SBOMs directly from firmware binaries and keeps them audit-ready across versions, without source code.
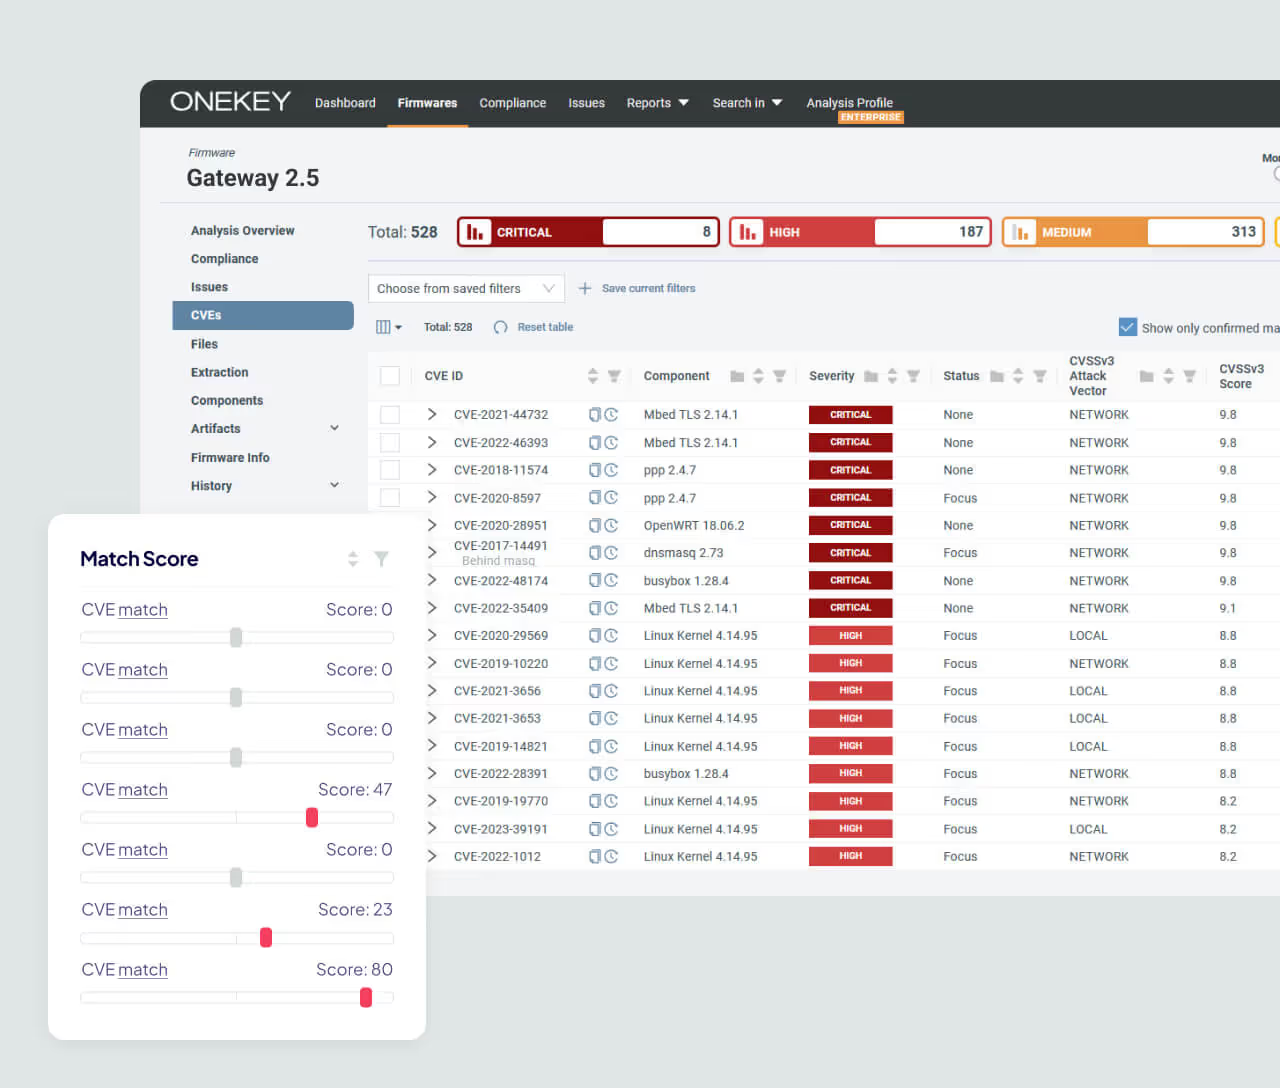
Vulnerability Management
ONEKEY matches components to CVEs, prioritizes real exploitability with VEX, and links remediation to the evidence your compliance workflows require.
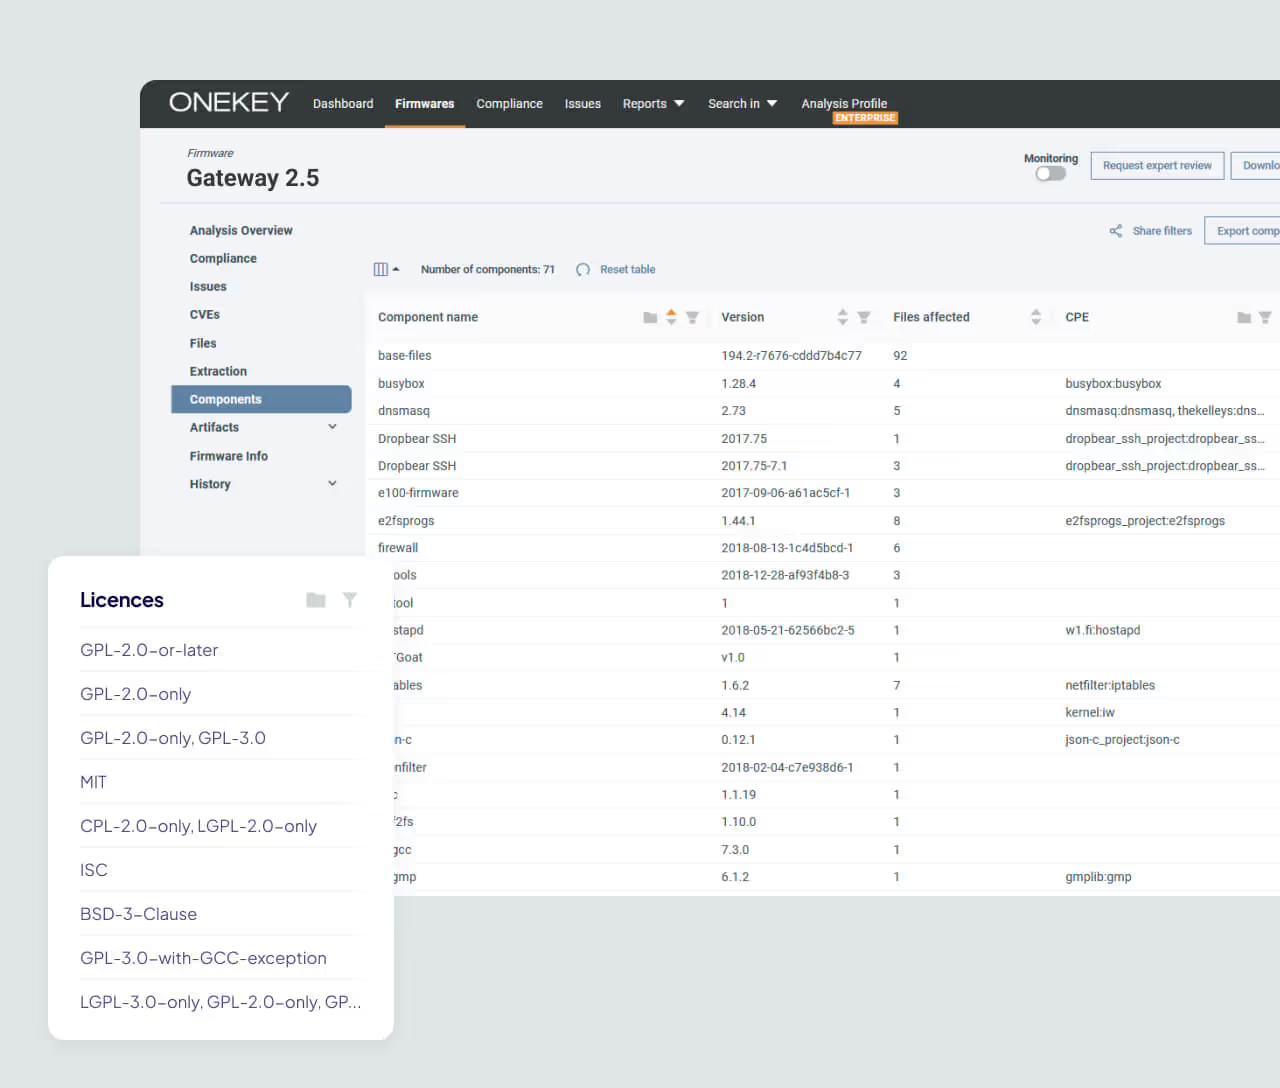
License Management
ONEKEY detects open-source and third-party licenses in firmware and flags obligations and conflicts before they turn into legal or compliance findings.
FAQs
Get detailed answers to the most common questions on safeguarding your connected products.

What is firmware security compliance?
Firmware security compliance is the process of proving that firmware meets cybersecurity regulations, standards, and internal requirements. It covers component visibility, vulnerability handling, secure configuration, monitoring, and audit evidence. For connected products, it must be tied to real firmware versions, not just company policies.
How is firmware compliance different from IT (GRC) compliance?
IT compliance usually focuses on enterprise systems, policies, access controls, and operational processes. Firmware compliance focuses on product software, embedded components, supplier binaries, SBOMs, vulnerabilities, and lifecycle evidence. It requires technical proof from the product itself.
Does the Cyber Resilience Act require firmware monitoring?
The CRA increases the need for lifecycle vulnerability handling and product security evidence. Firmware monitoring helps manufacturers detect new vulnerabilities, track affected versions, and maintain proof after release. This supports stronger readiness for CRA obligations.
How do you produce audit-ready compliance evidence for devices?
You produce audit-ready evidence by linking firmware analysis, SBOMs, vulnerability findings, remediation status, and requirement mappings. Automation helps keep this evidence current across products and versions. ONEKEY supports this with binary analysis, compliance workflows, and exportable documentation.
What is a Digital Cyber Twin?
A Digital Cyber Twin is a living, virtual view of your product's security and compliance status. It tracks firmware versions, known components, vulnerabilities, and changes after deployment, giving your team continuous oversight instead of one-time checks. It helps you spot compliance drift and new vulnerabilities before they affect a shipped product.


