Securing the Software Supply Chain for Connected Products
Your connected products ship with firmware, open-source libraries, supplier binaries, and legacy code that are hard to verify. Standard tools stop at the build pipeline. ONEKEY analyzes the firmware you actually ship, so you uncover hidden components, cut vulnerability noise, and prove compliance without relying on source code.
Industry Leaders Rely on ONEKEY


Why Product Teams Struggle to Secure the Software Supply Chain
Supply chain security is hard when you cannot see every component inside your product. Firmware often arrives from suppliers as a closed binary, with little proof of security, quality, or compliance. That creates a trust gap between what vendors declare and what your team can actually verify before you ship.
No Visibility into Third-Party & Open-Source Components in Firmware
Your firmware may include code from chipset vendors, open-source projects, suppliers, internal teams, and legacy product lines. Some of it is outdated, vulnerable, or licensed in ways that affect commercial use. You cannot manage these risks without knowing which components are present. Supplier files rarely include an SBOM.
Build-Pipeline Tools Miss the Shipped Binary
Build-pipeline tools help secure source code, dependencies, and CI/CD workflows. They do not always show what ended up in the final firmware image. Embedded products often include compiled binaries, vendor packages, and components added outside standard pipelines. A clean build report does not prove the shipped product is clean.
Regulatory Pressure Without Audit-Ready Evidence (CRA, IEC 62443)
Regulators and customers now expect stronger proof of product cybersecurity. CRA and IEC 62443 raise the pressure to show how you manage components, vulnerabilities, and lifecycle risk. Informal supplier claims are no longer enough. Your team needs clear, current evidence tied to real product versions, straight from the firmware.
How ONEKEY Secures the Software Supply Chain
Binary-Based Component Identification
A complete SBOM starts with real component visibility. ONEKEY generates SBOMs directly from firmware binaries, even when source code or supplier data is missing, so you know what is inside each product version. Compare declared components against what actually ships, and turn that visibility into ongoing supply chain control.

Built for Embedded/IoT/OT - Not Just App Pipelines
IoT and OT products need more than application security controls. They run on constrained hardware, long release cycles, supplier firmware, and field deployments that are hard to update. ONEKEY identifies known CVEs and zero-day patterns in firmware components, so your team finds real risks that app-pipeline tools miss.

Prove What Ships in Your Firmware
A clean build report does not prove what shipped. ONEKEY analyzes the final firmware and monitors it over time with a Digital Cyber Twin. Track new CVEs, compare releases, and see which supplier components carry risk. VEX-based prioritization cuts false-positive noise, so teams focus on vulnerabilities that affect the product.

Why ONEKEY Is the Best Choice for Software Supply Chain Security
ONEKEY is built for connected and embedded products, where source code, supplier data, and build-system access are not always available. It helps product, security, compliance, and development teams work from the same evidence. That shared product context is what real software supply chain decisions depend on.

Binary-Based Component Identification
Binary-based component identification shows what is actually inside your firmware. It uncovers open-source libraries, third-party packages, outdated components, and licensing risks, even when supplier data is incomplete. Use it before release and after deployment as a quality gate that stops risky code entering your products.

Built for Embedded/IoT/OT - Not Just App Pipelines
IoT firmware security focuses on the firmware image and device behavior. Software supply chain security covers the full chain of components, suppliers, SBOMs, vulnerabilities, and lifecycle evidence. Connected products need both views working together, and ONEKEY gives your team that combined picture on real hardware.

Prove What Ships in Your Firmware
Traditional SCA tools inspect source code, package manifests, and application dependencies. Pipeline tools secure development workflows and release automation. Both can miss binary-only firmware, supplier packages, and components added outside the main build. ONEKEY closes that gap with binary-level visibility into what shipped.
How ONEKEY Automates Software Supply Chain Verification
Supply chain checks often rely on supplier questionnaires, build reports, and SBOMs delivered as PDF attachments. None of these prove what is inside the firmware that reaches your customers. ONEKEY automates verification through binary-level analysis of the final firmware image, without source code or build-system access. You move from trusting vendor claims to a repeatable quality gate for every incoming component and release.
The process starts by uploading the firmware image into the platform, whether it comes from a supplier, a chipset vendor, or your own build. You do not need source code, build pipelines, or complete supplier documentation to begin. This is especially useful for closed third-party binaries and legacy product lines. Verification starts from the software actually shipped, not from what was declared.
ONEKEY analyzes the compiled firmware to generate a complete SBOM and identify open-source libraries, third-party packages, and outdated components. Known CVEs and zero-day patterns are detected alongside license risks that affect commercial use. Hidden and undeclared components surface even when they were added outside the standard build pipeline. Your team sees the full composition of every product version.
If a supplier delivered an SBOM, ONEKEY compares it against the discovered binary contents and flags missing components, version mismatches, and undocumented packages. Vulnerabilities are then prioritized with VEX-based assessment so your team focuses on findings that are actually exploitable in the product. Risky components can be blocked at the quality gate before they enter your products. The trust gap between vendor claims and shipped firmware closes.
Once analysis and validation are complete, the platform generates exportable SBOMs in CycloneDX or SPDX and evidence that supports CRA and IEC 62443 requirements. These reports can be shared with customers, regulators, and internal stakeholders as part of supplier reviews and compliance workflows. ONEKEY's Digital Cyber Twin then monitors each firmware version for new CVEs and composition changes. You maintain visibility across suppliers, releases, and the full product lifecycle.
FACTS & Figures
FACTS & Figures
Cut Security Costs by $400K+
With ONEKEY’s Quality Gate, SWISSCOM stops costly IoT security incidents before they happen – saving time, money, and trust.
100% Firmware Analysis
Analyze every firmware, component, and library for vulnerabilities, license issues, and outdated code—automatically.
15-Minutes Firmware Risk Check
From hidden vulnerabilities to outdated components—get clarity before they hit your supply chain.
Ship Cybersecure, Compliant Products with Confidence
ONEKEY helps your team secure connected products from integration to deployment. Generate SBOMs, detect known and zero-day vulnerabilities, manage compliance evidence, and monitor firmware continuously in one platform. It builds a stronger foundation for secure releases and long-term product resilience across every version.

Why Customers Trust Us

“ONEKEY helps us to uncover critical vulnerabilities in embedded devices in a fully automated way. This allows us to target manual testing efforts more efficiently on business logic issues.“

“We use ONEKEY to check every piece of software for potential risks before it even reaches release candidate status, at which point any issues are immediately analyzed and fixed. This allows us to effectively secure new features and interfaces.”

“We provide best-in-class services to our IoT customers, helping them ensure security throughout their entire product lifecycle. So naturally we want to deliver continuous firmware monitoring and vulnerability assessments using the best tools and solutions in the business. ONEKEY's automated firmware analyses help us to deliver our services efficiently and with unparalleled quality.“

“ONEKEY’s automated binary software analysis simplifies product security at Snap One by reducing manual efforts while increasing transparency and confidence. We enjoyed a smooth onboarding experience and highly recommend the excellent support from a team of experts.”


“ONEKEY’s capabilities and security expertise made it a truly eye-opening experience to work with them.”

Secure Every Link in Your Software Supply Chain
Supply chain security does not end with component visibility. ONEKEY adds zero-day detection, compliance mapping, and license management on top of the same firmware analysis, so one upload covers security, legal, and regulatory review. Product, security, and compliance teams decide from a single source of truth.
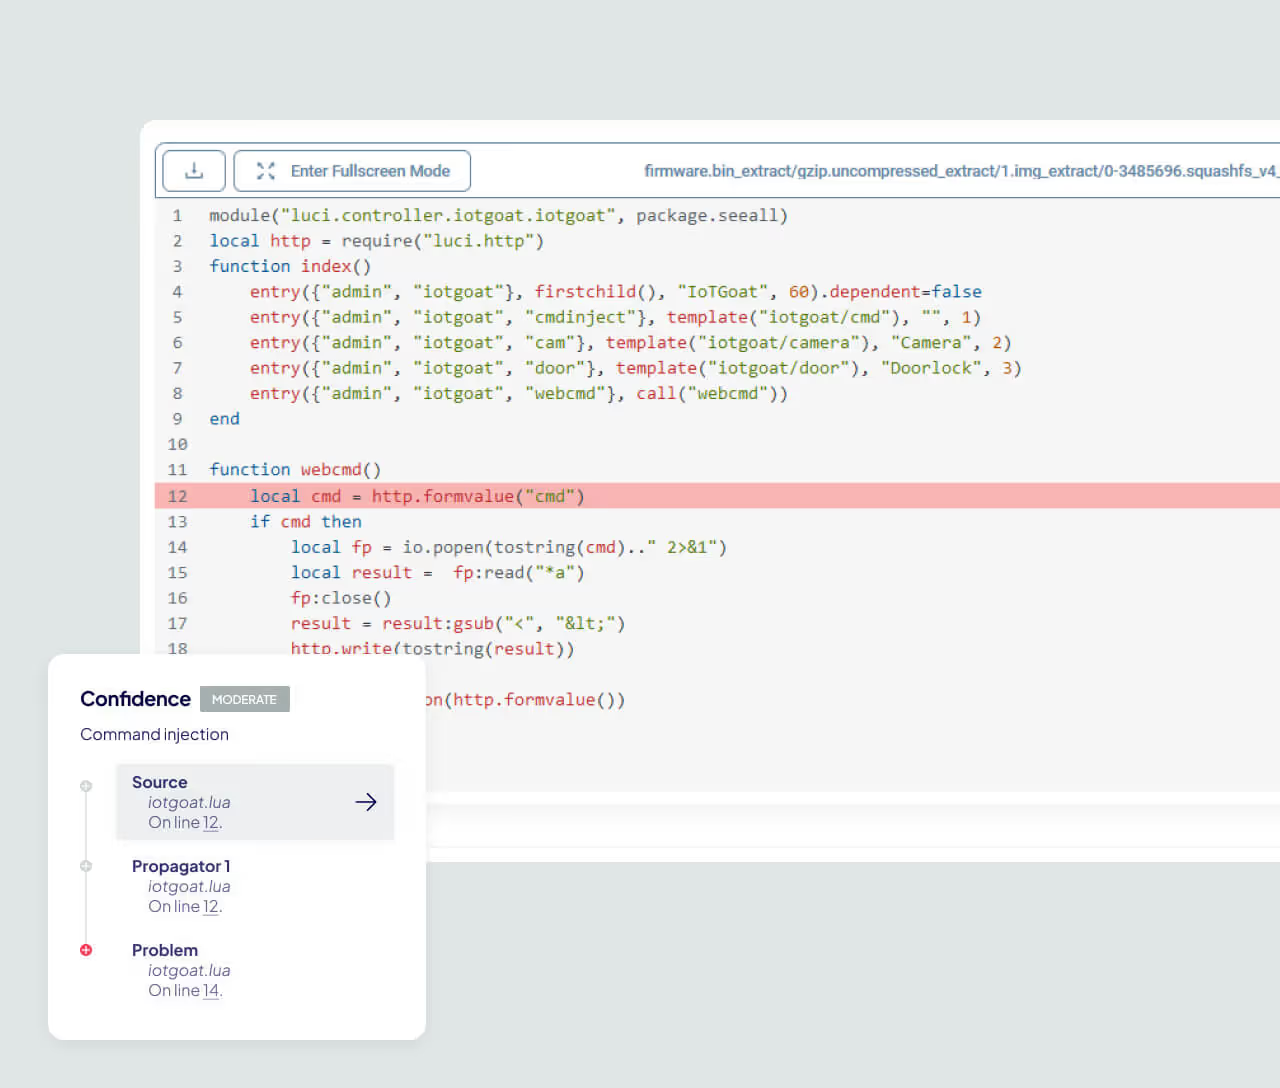
Zero-Day Detection
ONEKEY detects unknown vulnerabilities and insecure patterns in supplier and in-house firmware, so critical weaknesses surface before they appear in public CVE feeds.
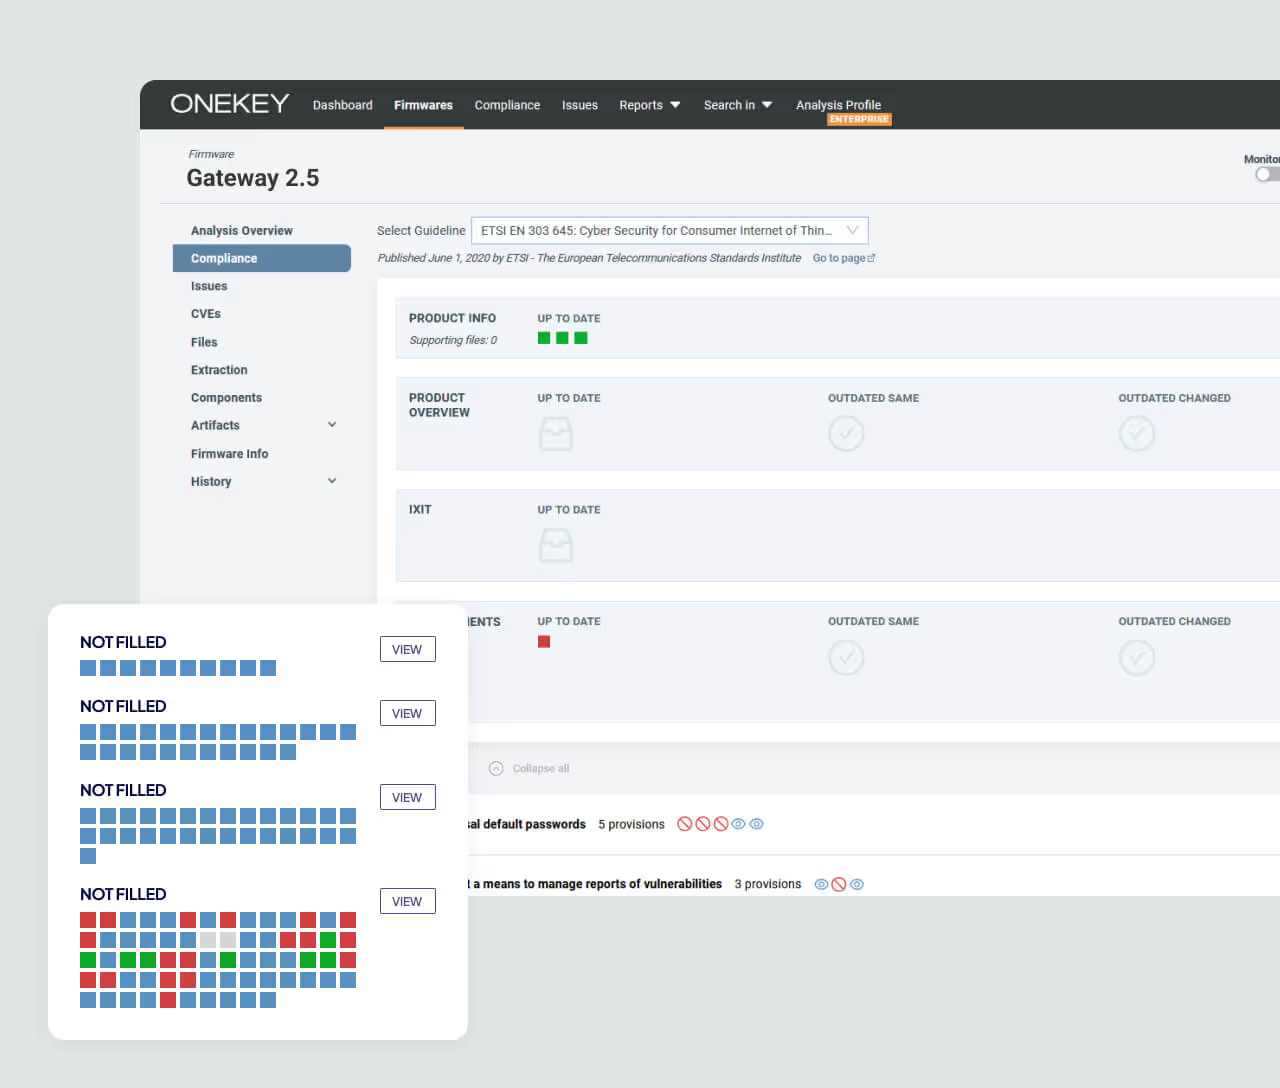
ONEKEY Compliance Wizard
The Compliance Wizard maps supply chain findings to CRA, IEC 62443, RED, and other standards and exports audit-ready evidence bundles for customers and regulators.
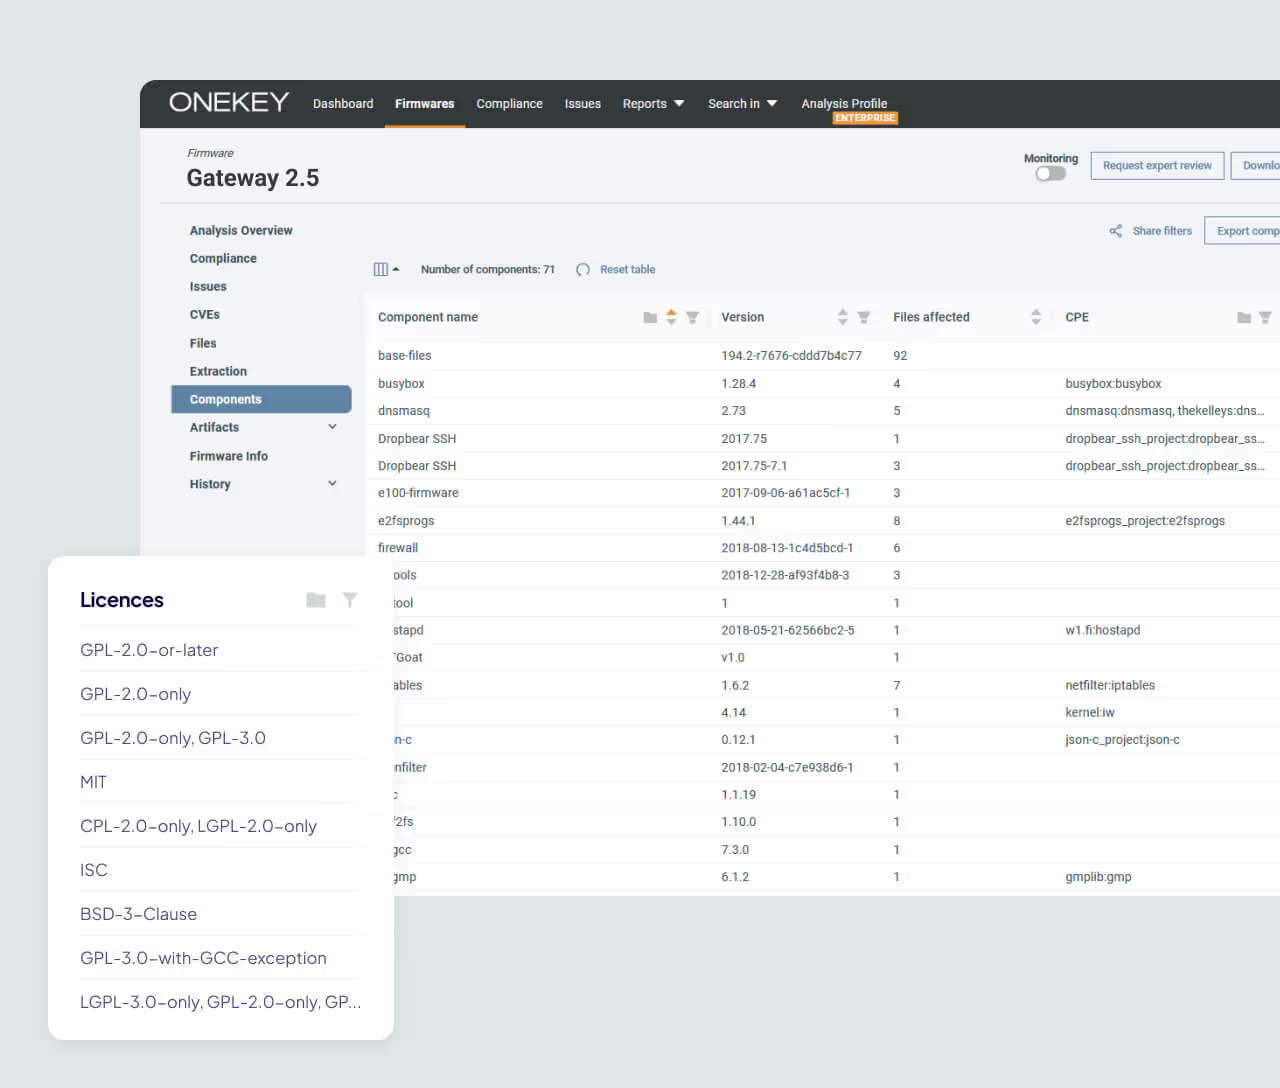
License Management
ONEKEY identifies open-source and third-party licenses in supplier firmware and flags obligations and conflicts before products ship.
FAQs
Get detailed answers to the most common questions on safeguarding your connected products.

What is software supply chain security software?
Software supply chain security software helps you identify, assess, and manage risks in the components used to build and ship products. For connected products, this includes firmware, open-source packages, supplier binaries, and third-party modules. It helps your team understand what is inside each product and which risks need action.
How is it different from SCA / application security tools?
SCA and application security tools usually focus on source code, package manifests, and development pipelines. ONEKEY focuses on firmware binaries and shipped product content, which is critical for embedded, IoT, and OT environments. This helps your team find risks that may not appear in pipeline data.
How does an SBOM improve software supply chain security?
An SBOM shows which components are inside your product. It helps your team track versions, identify vulnerabilities, assess supplier risk, and respond when new CVEs appear. A binary-generated SBOM is especially useful when source code or supplier records are missing.
Can the software supply chain be secured without source code?
Yes, binary analysis can help secure the software supply chain without source code. ONEKEY analyzes firmware binaries to identify components, vulnerabilities, licensing risks, and security-relevant details. This gives your team visibility even when supplier files arrive as closed black boxes.


